

Risk-based authentication is about judging whether the request seems reliable enough to continue, utilizing contextual indicators corresponding to system posture, location, behaviour, and different indicators. Cryptographic authentication verifies that the patron is tied to the session or transaction by way of cryptographic proof before the data is trusted. Risk-based authentication estimates legitimacy from patterns, system alerts https://joomline.net/ru/forum/other-plugin/5839-convead-joomla-virtuemart.html, and other personal-data driven indicators. The first establishes stronger identification assurance up front, whereas the second makes a probabilistic judgment that can be weaker under privateness constraints. A passkey supplier is answerable for the creation and passkey management of a user’s passkeys. The primary use case for passkeys is changing the password because the first/primary factor for account authentication.
Secure Your Future With Entrust
For instance, your cellphone may be linked to your laptop, allowing you to use a passkey from your telephone to signal into a service in your laptop computer. They inherently help cut back attacks from cybercriminals similar to phishing, credential stuffing, and other remote assaults. With passkeys there aren’t any passwords to steal and there’s no sign-in information that can be used to perpetuate assaults. Traditional phishing assaults succeed because authentication secrets and techniques are moveable.
- Some cryptographic units do not truly bind to the protected session secrets and are due to this fact not verifier impersonation resistant.
- That makes it higher suited to transactions where authenticity must be demonstrable after the fact, or the place an attacker might otherwise try to reuse a stolen session, token, or approval path.
- Multi-factor authentication raised the bar, however adversary-in-the-middle (AiTM) toolkits like Evilginx and Tycoon 2FA simply relay the second factor in actual time.
- In self-organized vehicular ad hoc networks (VANETs), mutual authentication is achieved without a central CA; each participant maintains its personal certificates key-pair and indicators others’ keys, forming a dynamically evolving certificates graph.
Signature Verification On The Server
Each extensions are optional in the specification, and assist varies across browsers and authenticator hardware. Functions that depend upon them must examine for availability at registration time and degrade gracefully when the extensions are absent. As browser and authenticator support matures, these primitives might considerably enhance key administration for client-side cryptography on the net. These are two separate enforcement points, and neither is under application-level or attacker control.
Biometrics can be verified centrally, though will increase in processor performance (e.g., in mobile devices) makes it increasingly sensible to verify biometrics on the sensor location. If central verification is performed, further requirements about the security of the biometric information in transit and authentication of the sensor/endpoint are imposed. In particular, use of a biometric is required to be tightly bound to specific device(s) for which the sensor and endpoint have been determined by the verifier to satisfy the required performance parameters.
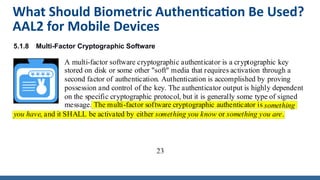
Under the unique WebAuthn specification, every area requires its own credential. The layered verification is the explanation the protocol is taken into account phishing-resistant by specification somewhat than merely by intent. The traditional examples of multi-factor cryptographic authenticators are US Government PIV and Department of Defense CAC authenticators. Other “smart card” authenticators, such as the Estonian e-resident card, are additionally in this category. Multi-factor cryptographic gadgets can additionally be embedded in endpoints, as is the case of FIDO UAF authenticators. FIDO adds elements to key pair authentication by locking the credential and requiring the person to unlock it with the same mechanism used to unlock the gadget, i.e.
B423 Use Of Biometrics
Accordingly, the verifier ought to accept any of several possible future one-time passwords, and advance its state to the authenticator output most lately used when a profitable authentication is performed. An instance of cryptographic authentication with a fusion credential could be discovered in this GitHub repository. An example of cryptographic authentication with a fusion credentialcan be found on this GitHubrepository. Yes, FIDO Safety Keys contain device-bound passkeys since 2019, when FIDO2 added support for passwordless sign-ins by way of discoverable credentials with person verification. All the shopper platforms and browsers have native support to exercise security keys already. Safety key distributors may choose to assist passkey synchronization sooner or later.
What Is Cryptography In Security?
The flags byte encodes whether or not person presence (UP) was confirmed (the user touched the authenticator or interacted with a biometric prompt) and whether consumer verification (UV) was carried out (a PIN was entered or a biometric matched). Contemplate an attacker who units up a convincing replica of financial institution.example.com at bank-examp1e.com. A user navigates to the phishing web site and triggers a passkey authentication flow. Relying get together ID (rpId) is a site string chosen by the service at registration time. It is often the registrable area of the site (for instance, instance.com quite than login.example.com). The rpId is hashed with SHA-256 and embedded instantly into the authenticator data structure that the authenticator indicators during each registration and authentication ceremonies.
The resultant of authentication is a key-exchange which then can be utilized for different cryptographic providers. The other suggestion is a remark in Example 2, stating that ‘challenge’ and ‘domain’ shield agaisnt replay assaults. It is not clear why a replay assault could be of concern when transmitting a presentation, so perhaps “replay attack” actually means “man-in-the-middle attack”.