

By evaluating the text-crypto text pairs, the opponent attempts to find the secret key to make use of to decrypt all subsequent messages (Zimba et al., 2020). It may be fairly difficult for an adversary to gain possession of a quantity of text-ciphertext pairs. Even protocols that declare to supply encryption, such as SSL or early versions of TLS, may be insecure if misconfigured or outdated. Strong data-in-transit protections require the newest variations of safe protocols, proper certificates management, and enforcement of communication only over encrypted channels. Failure at any stage of the info transmission path leaves organizations open to interception assaults like sniffing, replay, or man-in-the-middle.
- Automating these processes through key management companies (KMS) or centralized coverage engines reduces the chance of human error.
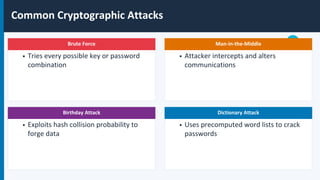
- Birthday assaults exploit the probability of two completely different inputs producing the identical hash worth, often identified as a collision.
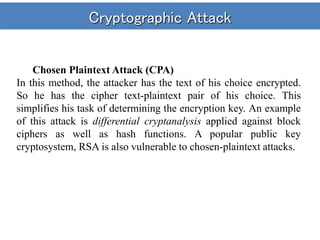
- An assault based mostly on the selected exposed text is a chance much more serious possibility for the transmitting parties (Kumar et al., 2018).
- You Are being tested on your capability to establish vulnerabilities, suggest applicable countermeasures, and clarify the connection between attack vectors and defensive mechanisms.
Frequently Requested Questions
When you’re finished with this course, you’ll have the skills and information of attacks on cryptographic applications and protocols wanted to implement stronger cryptographic protocols to secure data. In order to attain it, they maintained secrecy about encryption algorithms and encryption machine devices and thoroughly examined the reliability of personnel who had access to cryptosystems. Nevertheless, already in the XIX century, specialists within the field of cryptography advised that the secrecy of encryption algorithms is not a assure in opposition to hacking (Lou et al., 2021). Moreover, it was realized that a very dependable encryption system should stay safe even when an opponent fully recognizes the cryptographic algorithm. Storage, transmission, and transformation of data are subjected to various assaults.
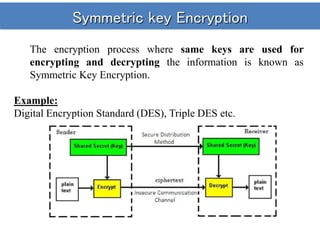
Repository containing my Sage and/or Python implementations of attacks on well-liked ciphers and public key cryptosystems. Cryptography includes methods for secure communication, making certain that only the sender and intended recipient can perceive the transmitted data. It has keys for encryption (transforming plaintext into unreadable ciphertext) and decryption (reverting ciphertext back to readable form).
There are additionally miscellaneous factoring attacks, which may be applicable for concentrating on many public key schemes, and a few notes on topics corresponding to elliptic curve pairings. I plan to complete all present public key attacks sooner or later and considerably expand assault help for symmetric key primitives, as the latter has been relatively lacking for the previous few years. The cryptanalyst can have particulars about the format of the encrypted file, for instance, knowing that it is a JPEG image file or a Word or Excel doc; all of them comprise particular commonplace headers or fragments. Thus, the professional in cryptanalysis shall be capable of producing the important data for an attack primarily based on the identified uncovered text. An assault primarily based on the selected exposed text is a possibility much more severe option for the transmitting events (Kumar et al., 2018).
These services also can support “virtual patching” when cryptographic libraries or software parts require pressing remediation. To improve detection and response, Cloud Network Analytics supplies visitors visibility and anomaly detection that may assist determine suspicious patterns in maintaining with downgrade attempts, MITM probing, or credential abuse. Together, these capabilities assist organizations enforce stronger encryption practices and cut back the probability that cryptographic weaknesses will become exploitable safety gaps. Cryptographic failures often stem from weak configurations, outdated protocols, insecure knowledge dealing with, or inconsistent enforcement throughout complicated environments.
Places Discover Radware’s Workplaces And Powerful World Presence
If encryption keys are improperly generated, saved, distributed, or rotated, even robust cryptographic algorithms turn into ineffective. Hardcoding keys in supply code, sharing them via https://www.filmwritten.org/how-medical-app-development-is-transforming-healthcare-in-2025.html unencrypted channels—or failing to retire keys after worker turnover or compromise events—all introduce avoidable danger and weaken system safety. As of yet, there are implementations for assaults against RSA, Diffie-Hellman and its elliptic curve variant, AES-ECB, and AES-CBC.
To install on Ubuntu and other Linux distros, I imagine sudo apt install sagemath, or one thing along those traces will get the job done.
Cryptographic Failures: Impression, Root Causes & Examples
In this case, the cryptanalyst is enabled to use the “text-cryptotext” pairs offered to him and kind the texts he wants himself and encrypt them with the specific key he intends to detect. Radware Alteon Application Delivery Controller (ADC) plays a central role in strengthening TLS hygiene by enabling centralized SSL/TLS offloading, policy enforcement, and certificate lifecycle management. By standardizing TLS variations and cipher suite settings at the edge, Alteon helps forestall insecure downgrade eventualities and reduces exposure to inconsistent encryption across backend providers.
The major safety violations are disclosure of knowledge values, lack of confidentiality, modification with out authorization, or unlawful loss of access to those property. A passive assault is an action during which the adversary has no capability to change transmitted messages. Under a passive attack, it is just possible to intercept sent messages, decrypt them and analyze the site visitors (Kumar et al., 2018). The opponent can change transmitted messages in an energetic assault and even contribute his own messages. Side-channel assaults exploit data leaked through system habits rather than cryptographic flaws. Timing differences, memory access patterns, or physical emissions can reveal secrets when implementations depend on delicate information.